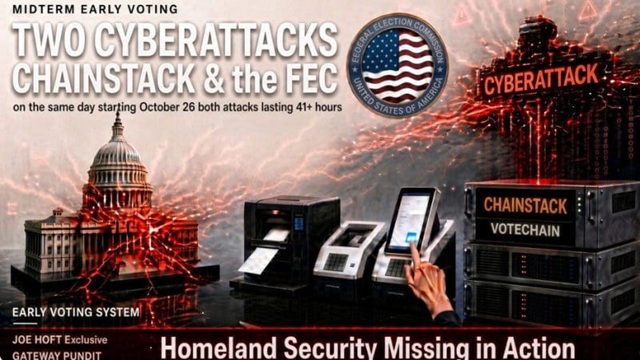
The CyberAttack that Hit the FEC Also Hit the Voting Firm “CHAINSTACK” which has an application that Connects Networks to Submit and Retrieve Vote Counts
The CyberAttack that Hit the FEC Also Hit the Voting Firm “CHAINSTACK” which has an application that Connects Networks to Submit and Retrieve Vote Counts.
CyberATTACK – HACKED CHAINSTACK introduces a hypothetical voting application called VoteChain, designed to operate across multiple blockchain networks. The imagined application would connect to those networks to submit votes or retrieve vote counts.
The election argument is already at a boil. Pollsters and commentators debate war, immigration, and affordability as the bloodbath of the midterm elections. Others point to “impossible numbers,” “unlikely results,” fraud, or a stolen election. Charts circulate, accusations harden, and everyone’s hair is on fire.
Set the arguments aside for a moment. Examine the advanced technology—and the cybersecurity incidents—unfolding during early voting on the same day.
On the night of October 26, 2026, the Federal Election Commission’s electronic-filing system went dark. That same date appears in another company’s incident report: Chainstack says an attacker entered its software-development environment on October 26, then reached parts of its live production infrastructure three days later.[reuters][chainstack]
The central issue is the access point.
But access to what? Even if an attacker reached a state’s results-reporting system, how could that translate into changes across multiple states? Don’t states and local jurisdictions operate their own equipment and reporting systems?
They do, and a results website is not the same as the equipment that counts votes. The critical question is which system an attacker reached and what that access allowed.[eac][eac]